 By Aditya Agarwal
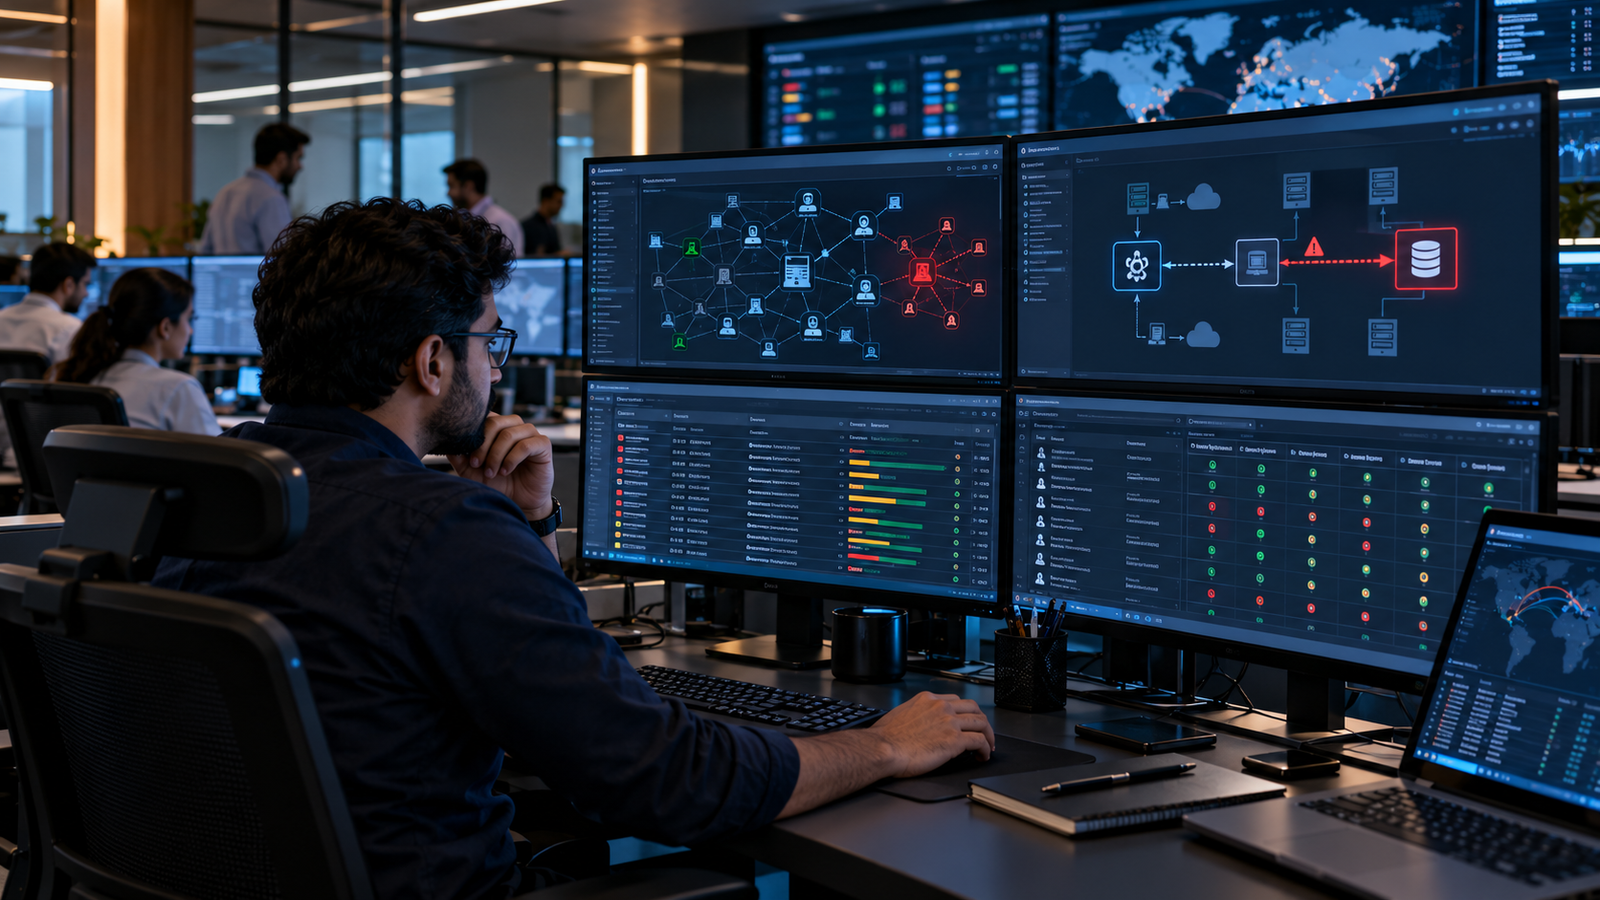
AI agent security is becoming a priority for enterprise technology teams as businesses deploy autonomous systems that can access data, interact with software and carry out multi-step tasks.
Microsoft announced expanded capabilities for Project Perception on 19 October 2026, introducing additional tools intended to help organisations monitor AI agents and adjust their permissions as their behaviour and risk change. The update includes capabilities associated with Microsoft 365 E7 and Agent 365. (Microsoft Security Blog)
Why AI Agents Need Different Security Controls
Traditional software generally follows predefined instructions, while AI agents can interpret requests, choose tools and perform sequences of actions to complete a task.
This flexibility can improve productivity, but it also creates security challenges. An agent may encounter unexpected information, receive malicious instructions or attempt an action beyond its intended purpose.
If an agent has broad access to company files or applications, a mistake or compromise can have consequences beyond the original task.
Microsoft’s approach treats AI agents as potential insiders whose permissions and behaviour must be monitored rather than assuming that an agent remains trustworthy after deployment.
How Project Perception Works
Microsoft describes Project Perception as a security system that coordinates specialised AI agents to help identify risks, investigate suspicious activity and support remediation.
The system uses signals across areas such as identity, data, endpoints, cloud services, networks and agent activity to build a picture of risk.
The expanded capabilities include Dynamic Agent Risk, which assesses changes in an agent’s risk profile. Other controls are designed to adjust permissions and access policies in response to that risk.
The objective is to help security teams understand what an agent is doing, what information it can reach and whether its current level of access remains appropriate.
Guardian Agents and Automated Response
Microsoft also introduced Guardian Agents and security playbooks designed to help security teams respond to changing threats.
Playbooks can define intended security outcomes and coordinate protective actions. Guardian Agents can assist with investigation, explain why risk levels have changed and recommend or carry out containment within defined policy boundaries.
Human oversight remains important, especially when a response could interrupt business operations or affect sensitive data.
Automation can help security teams react more quickly, but organisations still need clear rules governing which actions an AI security system may take independently.
Why This Matters for Indian Businesses
Indian companies are increasingly exploring AI agents for customer service, software development, financial operations and internal administration.
As deployments expand, businesses need to manage agent identities, restrict access to confidential information and maintain records of important actions.
Useful safeguards include:Granting agents only the permissions needed for their tasks.Keeping testing environments separate from production systems.Logging agent activity and reviewing suspicious behaviour.Requiring human approval for high-impact actions.Revoking access when an agent no longer needs it.
These practices can reduce exposure even when organisations use security products from different vendors.
What Businesses Should Evaluate
Companies considering enterprise AI security tools should examine how the system discovers agents, integrates with existing identity controls and handles changing permissions.
They should also evaluate false positives, incident-response workflows, compatibility with existing systems and the level of human oversight required.
A security platform’s announced capabilities do not guarantee that every threat will be detected or contained. Implementation, configuration and ongoing monitoring remain essential.
Outlook
Microsoft’s Project Perception update reflects a broader shift in enterprise cybersecurity: AI agents must be managed as active participants in business systems, not simply as another application.
As organisations adopt more autonomous workflows, the ability to monitor behaviour and restrict access dynamically could become increasingly important.
For businesses, the core requirement remains straightforward: AI systems should receive only the authority necessary to complete their tasks, and that authority should be reviewed as risk changes.
Tags: AI agent security, Microsoft Project Perception, enterprise AI, cybersecurity, Microsoft Agent 365, artificial intelligence
Internal Link Suggestion: FlairiusNews — AI Technology and Cybersecurity News
Outbound Sources:
- Microsoft Security Blog — Project Perception Update
- The Indian Express — Microsoft Expands Project Perception