 By Raghav Sharma
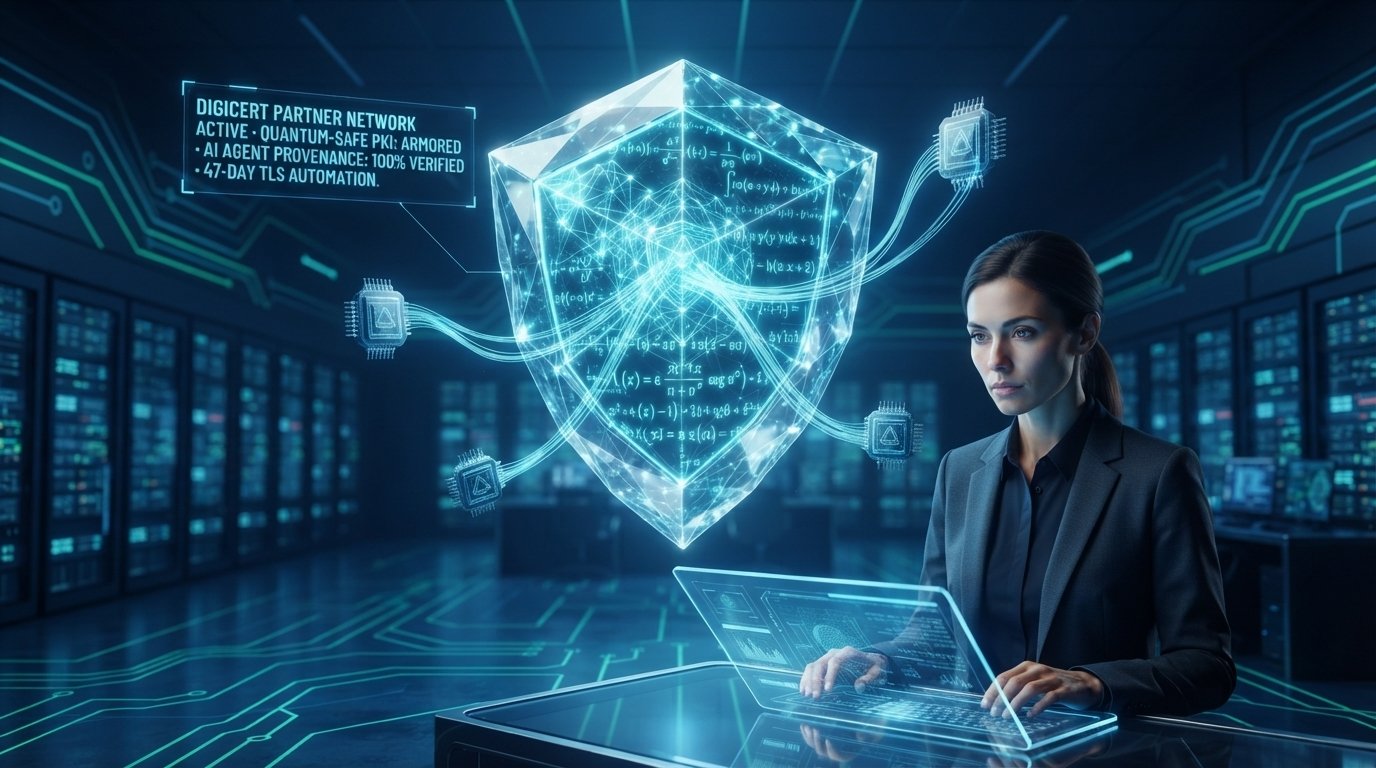
Enterprise technology faces two simultaneous architectural challenges in late 2026. On one hand, autonomous AI agents now execute sensitive financial transactions and edit source code without human intervention. On the other hand, rapid advancements in quantum computing threaten to break classical RSA cryptography standards within a few years.
To solve both vulnerabilities, digital trust leader DigiCert launched its global Partner Network. Built on the DigiCert ONE platform, the initiative provides managed service providers and systems integrators with tools to govern autonomous AI agents, automate certificate lifecycles, and transition corporate infrastructure to post-quantum cryptography.
Consequently, the digital security perimeter is shifting from passive firewalls to cryptographic provenance. Enterprises must verify not just human identities, but the mathematical integrity of every autonomous algorithm operating within their tech stacks.
The Identity Crisis of Autonomous Software Agents
The rapid adoption of agentic software created a governance blind spot. When autonomous bots access sensitive customer records or trigger automated wire transfers, traditional security tools treat them as standard user accounts.
However, if an unauthorized actor tampers with model weights or injects malicious prompts, compromised agents can exfiltrate proprietary data undetected. Therefore, corporate security officers require cryptographic proof for every automated decision.
DigiCert solves this by embedding verifiable digital signatures directly into model weights and software supply chains. Through specialized PKI architectures, enterprise teams verify the provenance, authority, and authorized operational boundaries of every AI agent before it executes tasks.
Preparing for the Quantum Decryption Threshold
Beyond artificial intelligence governance, the network addresses the looming post-quantum transition. Cybersecurity analysts warn that malicious state actors actively harvest encrypted corporate communications today, intending to decrypt the data once scalable quantum processors emerge.
Furthermore, public TLS certificate validities are shortening to just 47 days, making manual key renewals impossible. The new MSP framework automates discovery, issuance, and policy enforcement across hybrid cloud environments.
Through DigiCert Quantum Central, IT departments inventory vulnerable legacy cryptographic assets and map automated remediation schedules. As a result, corporations swap vulnerable algorithms for quantum-resistant ciphers without interrupting daily operations.
Turning Compliance into Services-Led Revenue
The Partner Network spans six distinct commercial models, including global systems integrators, cloud marketplace providers, and managed service partners. Rather than selling one-off SSL certificates, security providers build recurring revenue streams around digital trust transformations.
Additionally, verified model provenance provides companies with regulatory immunity. As governments enforce algorithmic accountability standards, corporations with cryptographically audited AI systems can prove model integrity easily during regulatory audits.
The era of trusting software by default has concluded. By combining post-quantum cryptography with autonomous agent verification, DigiCert is constructing the mathematical armor required for the next decade of computing.
Tags: DigiCert 2026, Post Quantum Cryptography, AI Trust, Autonomous Agent Governance, PKI Modernization, Cybersecurity Trends, Digital Trust Author CTA: Follow Flairius News — sharp takes on AI, business, and India’s startup economy — flairiusnews.com
 Aditya Agarwal
 Ahana Verma